Introduction to Malware Analysis with Packet Capture Seminar
October 29, 2026
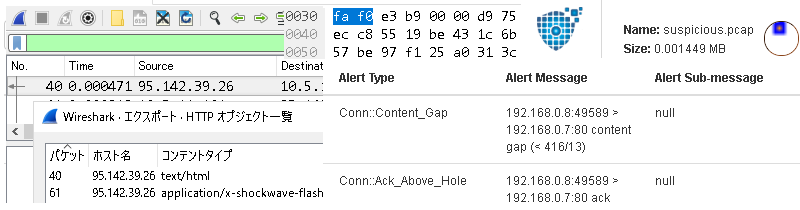
Learn the fundamentals and practical skills of malware analysis using packet captures in this hands-on seminar designed for beginners. Using Wireshark and real-world infected packets from malware such as LOKIBOT, Emotet, RAMNIT, Trickbot, and Exploit kits, participants will practice analyzing malware behavior, infection routes, device identification, root cause analysis, and creating incident reports. Attendees will receive analysis packets, materials, a CD-ROM, USB memory stick, a bag, and a boxed sushi lunch. Equipment such as servers for exercises is provided. For details and registration, please visit the organizer’s official website.




Comments 0
Sign in to leave a comment.